
Provides readers with a solid foundation in Arm assembly internals and reverse-engineering fundamentals as the basis for analyzing and securing billions of Arm devices
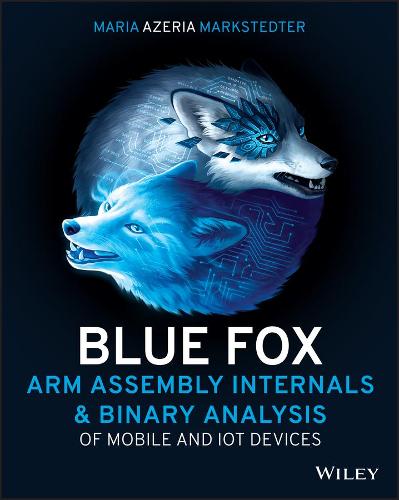
Finding and mitigating security vulnerabilities in Arm devices is the next critical internet security frontier-Arm processors are already in use by more than 90% of all mobile devices,billions of Internet of Things (IoT) devices,and a growing number of current laptops from companies including Microsoft,Lenovo,and Apple. Written by a leading expert on Arm security,Blue Fox: Arm Assembly Internals and Reverse Engineering introduces readers to modern Armv8-A instruction sets and the process of reverse-engineering Arm binaries for security research and defensive purposes.
Divided into two sections,the book first provides an overview of the ELF file format and OS internals,followed by Arm architecture fundamentals,and a deep-dive into the A32 and A64 instruction sets. Section Two delves into the process of reverse-engineering itself: setting up an Arm environment,an introduction to static and dynamic analysis tools,and the process of extracting and emulating firmware for analysis. The last chapter provides the reader a glimpse into macOS malware analysis of binaries compiled for the Arm-based M1 SoC. Throughout the book,the reader is given an extensive understanding of Arm instructions and control-flow patterns essential for reverse engineering software compiled for the Arm architecture. Providing an in-depth introduction into reverse-engineering for engineers and security researchers alike,this book:
- Offers an introduction to the Arm architecture,covering both AArch32 and AArch64 instruction set states,as well as ELF file format internals
- Presents in-depth information on Arm assembly internals for reverse engineers analyzing malware and auditing software for security vulnerabilities,as well as for developers seeking detailed knowledge of the Arm assembly language
- Covers the A32/T32 and A64 instruction sets supported by the Armv8-A architecture with a detailed overview of the most common instructions and control flow patterns
- Introduces known reverse engineering tools used for static and dynamic binary analysis
- Describes the process of disassembling and debugging Arm binaries on Linux,and using common disassembly and debugging tools
Blue Fox: Arm Assembly Internals and Reverse Engineering is a vital resource for security researchers and reverse engineers who analyze software applications for Arm-based devices at the assembly level.
Publisher: John Wiley & Sons IncISBN: 9781119745303Number of pages: 480Weight: 658 gDimensions: 234 x 185 x 28 mm
Kommentar